
Deep dive
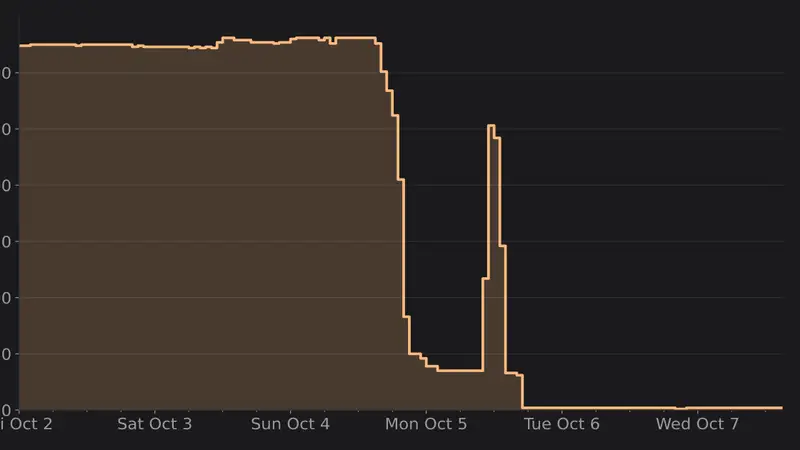
Attackers compromised 333 Tor exit nodes to intercept SSH connections
Attackers installed an OpenSSH backdoor on 333 Tor exit nodes and redirected SSH connections for interception after gaining access two months earlier. The account offers concrete lessons about relay trust, credential theft and incident response.
- What• Attackers compromised 333 Tor exit nodes and used them to intercept SSH connections.
- How• The nodes redirected SSH traffic to 12 interception servers, where attackers could steal passwords, observe commands and infect servers with Ebury.
- Why it matters• SSH host-key warnings and the trust placed in exit relays matter when designing secure remote-access systems.
